Amazon Redshift Compliance Management
Amazon Redshift Compliance Management involves more than protecting a data warehouse from unauthorized access. Organizations must continuously control permissions, identify regulated information, retain audit evidence, review security policies, and demonstrate that these controls remain effective as users and workloads change.
Amazon Redshift provides native capabilities for managing these requirements. Role-based access control, row-level security, Dynamic Data Masking, database audit logging, encryption, CloudTrail, and AWS compliance resources establish a capable foundation. AWS also includes Amazon Redshift within multiple compliance programs, including SOC, PCI, HIPAA, and FedRAMP. ([AWS Documentation][1])
However, maintaining data compliance becomes increasingly complex as schemas expand and sensitive information appears in new locations. Effective compliance management therefore requires an ongoing process that connects access control, data classification, activity monitoring, protection, and reporting.
This article explains how to manage Amazon Redshift compliance with native AWS capabilities and how DataSunrise can extend this framework with centralized and automated compliance controls.
Importance of Compliance Management
Amazon Redshift often consolidates large volumes of analytical data from multiple business systems. These datasets may contain personally identifiable information, financial records, payment data, healthcare information, authentication details, and other regulated content. As data volumes and user access grow, maintaining consistent compliance controls becomes more difficult.
Effective compliance management helps organizations maintain continuous control over how sensitive information is stored, accessed, monitored, and protected. It also supports requirements associated with regulations and standards such as GDPR, HIPAA, PCI DSS, and SOX.
For Amazon Redshift environments, compliance management typically requires organizations to:
- identify where regulated and sensitive data resides;
- enforce appropriate access controls and least-privilege permissions;
- monitor database activity involving sensitive objects;
- protect exposed values through masking and other security controls;
- retain reliable audit evidence for investigations and regulatory reviews;
- regularly reassess policies as schemas, users, and regulatory requirements change.
Without a continuous management process, compliance controls can gradually become outdated. New tables may introduce previously undiscovered sensitive data, users may retain unnecessary privileges, and monitoring policies may no longer reflect the current environment.
A structured compliance-management approach therefore connects data discovery, access governance, monitoring, protection, and reporting into an ongoing lifecycle. This reduces compliance gaps, improves audit readiness, and gives security teams clearer visibility into how regulated Amazon Redshift data is being used.
Native Amazon Redshift Compliance Management
Amazon Redshift includes several complementary security mechanisms that can support ongoing compliance management. Instead of treating access control, activity monitoring, encryption, and policy enforcement as separate tasks, administrators can combine them into a recurring process for reviewing permissions, protecting sensitive data, and retaining compliance evidence.
Review Roles and Database Privileges
Amazon Redshift supports role-based access control (RBAC), which allows administrators to assign permissions to roles rather than managing privileges separately for every user. This approach simplifies access administration in larger environments and supports the principle of least privilege.
For example, organizations can create a dedicated compliance role and grant access only to the required schema and tables:
CREATE ROLE compliance_reader;

GRANT USAGE ON SCHEMA compliance
TO ROLE compliance_reader;

GRANT SELECT ON ALL TABLES IN SCHEMA compliance
TO ROLE compliance_reader;
Administrators can review existing role relationships through the SVV_ROLE_GRANTS system view:
SELECT
    role_name,
    granted_role_name
FROM svv_role_grants
ORDER BY role_name;
Object-level permissions can be inspected through SVV_RELATION_PRIVILEGES:
SELECT
    identity_name,
    identity_type,
    namespace_name,
    relation_name,
    privilege_type
FROM svv_relation_privileges
ORDER BY namespace_name, relation_name;
These reviews help identify excessive privileges, obsolete role assignments, and access that no longer reflects current business responsibilities. Regular permission analysis is especially important in Redshift environments where users, teams, and analytical workloads change frequently.
Apply Data-Level Access Policies
Object-level permissions alone may not provide enough precision for regulated data. Amazon Redshift therefore includes additional controls such as row-level security and Dynamic Data Masking.
Row-level security allows organizations to restrict which records particular users or roles can retrieve from a table. For example, a basic RLS policy can restrict access according to a regional attribute:
CREATE RLS POLICY region_policy
WITH (region VARCHAR(20))
USING (region = current_user);
After creating the policy, administrators can attach it to the required table and role according to the organization's access model.
Dynamic Data Masking provides another layer of protection by changing how sensitive values appear in query results without modifying the underlying stored data. A masking policy can, for example, replace sensitive values with a constant:
CREATE MASKING POLICY mask_email
WITH (email VARCHAR(256))
USING ('***MASKED***');
Administrators can also inspect configured security policies directly:
SHOW RLS POLICIES;

SHOW MASKING POLICIES;
Periodic review is important because access requirements may change as schemas, job responsibilities, and data-processing purposes evolve.
Maintain Compliance Evidence Through Audit Logging
Access controls define what users are allowed to do, while audit records provide evidence of what actually happened. Amazon Redshift database audit logging captures several categories of activity that can support compliance investigations and reporting.
Connection logs record authentication attempts, connections, and disconnections. User logs capture changes to database user definitions, while user activity logs record executed SQL queries. For user activity logging, the corresponding parameter must be enabled:
enable_user_activity_logging = true
Administrators can also inspect recent connection activity through Amazon Redshift system views:
SELECT *
FROM sys_connection_log
ORDER BY record_time DESC
LIMIT 100;
Query-related activity can similarly be reviewed through Redshift system monitoring views:
SELECT
    user_id,
    query_id,
    query_text,
    start_time,
    end_time
FROM sys_query_history
ORDER BY start_time DESC
LIMIT 100;
Audit records can be exported to Amazon CloudWatch Logs or Amazon S3 for centralized storage and analysis.
At the AWS control-plane level, CloudTrail provides additional visibility into API operations performed against Amazon Redshift by users, IAM roles, and AWS services. Combined with database audit logging, this gives organizations both database-level and administrative activity evidence.
CloudWatch can be used for centralized log analysis and monitoring, while Amazon S3 can support longer-term audit retention. Together, these services help organizations maintain records required for security reviews, forensic investigations, and regulatory audits.
Protect Redshift Data with Encryption
Compliance management also requires protecting sensitive information from unauthorized disclosure. Amazon Redshift supports encryption at rest and integrates with AWS Key Management Service for encryption-key management.
Administrators can review important Redshift configuration information through system views when validating the environment:
SELECT
    current_database() AS database_name,
    current_user AS current_user;
AWS KMS activity can itself be monitored through CloudTrail, allowing administrators to review how encryption keys are used. This provides additional visibility into the security controls protecting regulated information.
Organizations should combine encryption at rest with encrypted network communications and appropriate network security controls. Amazon Redshift supports secure traffic for both provisioned clusters and Serverless environments, helping organizations protect data while it moves between clients and the data warehouse.
Encryption should therefore be treated as one component of a broader compliance framework rather than as an isolated control.
Review Compliance Responsibility
Amazon Redshift participates in multiple AWS compliance programs, but using a compliant AWS service does not automatically make an organization's workload compliant.
Under the AWS shared responsibility model, customers remain responsible for how they configure access, store regulated information, monitor activity, and apply controls according to their own regulatory obligations.
Administrators can perform periodic checks of important access and policy information using a compact set of queries:
-- Review role assignments
SELECT *
FROM svv_role_grants;

-- Review relation privileges
SELECT *
FROM svv_relation_privileges;

-- Review recent connections
SELECT *
FROM sys_connection_log
ORDER BY record_time DESC
LIMIT 50;

-- Review recent queries
SELECT *
FROM sys_query_history
ORDER BY start_time DESC
LIMIT 50;
As a result, compliance teams must continuously determine where sensitive data resides, who can access it, whether permissions remain appropriate, whether required activity is being logged, and whether audit evidence is retained for the necessary period.
They must also verify that security and compliance policies continue to match changing schemas, users, applications, and regulatory requirements. This ongoing administrative workload is one of the main challenges of native compliance management in large Amazon Redshift environments.
Amazon Redshift Compliance Management with DataSunrise
Native Amazon Redshift security provides a solid foundation for compliance through access controls, auditing, encryption, and policy enforcement. However, maintaining compliance across changing schemas, users, and sensitive datasets can require significant manual coordination.
DataSunrise adds a centralized compliance layer that combines Sensitive Data Discovery, Database Activity Monitoring, policy management, Risk Scoring, Dynamic and Static Data Masking, and reporting. For Amazon Redshift, the platform also supports native audit-log trailing through Amazon S3, Amazon CloudWatch, and Redshift Spectrum, allowing organizations to incorporate existing AWS audit infrastructure into a unified monitoring workflow.
Connect Amazon Redshift
The first step is to register the Amazon Redshift environment in DataSunrise. Administrators can configure the connection using supported Redshift authentication methods, including IAM authentication where required.
For environments where redirecting application traffic is undesirable, DataSunrise can use native audit-log trailing as an alternative monitoring approach. Audit data can be collected through Amazon S3, Amazon CloudWatch, or Redshift Spectrum, providing deployment flexibility while preserving visibility into database activity.
Once the instance is connected, administrators can apply DataSunrise auditing, discovery, masking, risk analysis, and compliance functionality from a centralized interface.
Discover Regulated Data
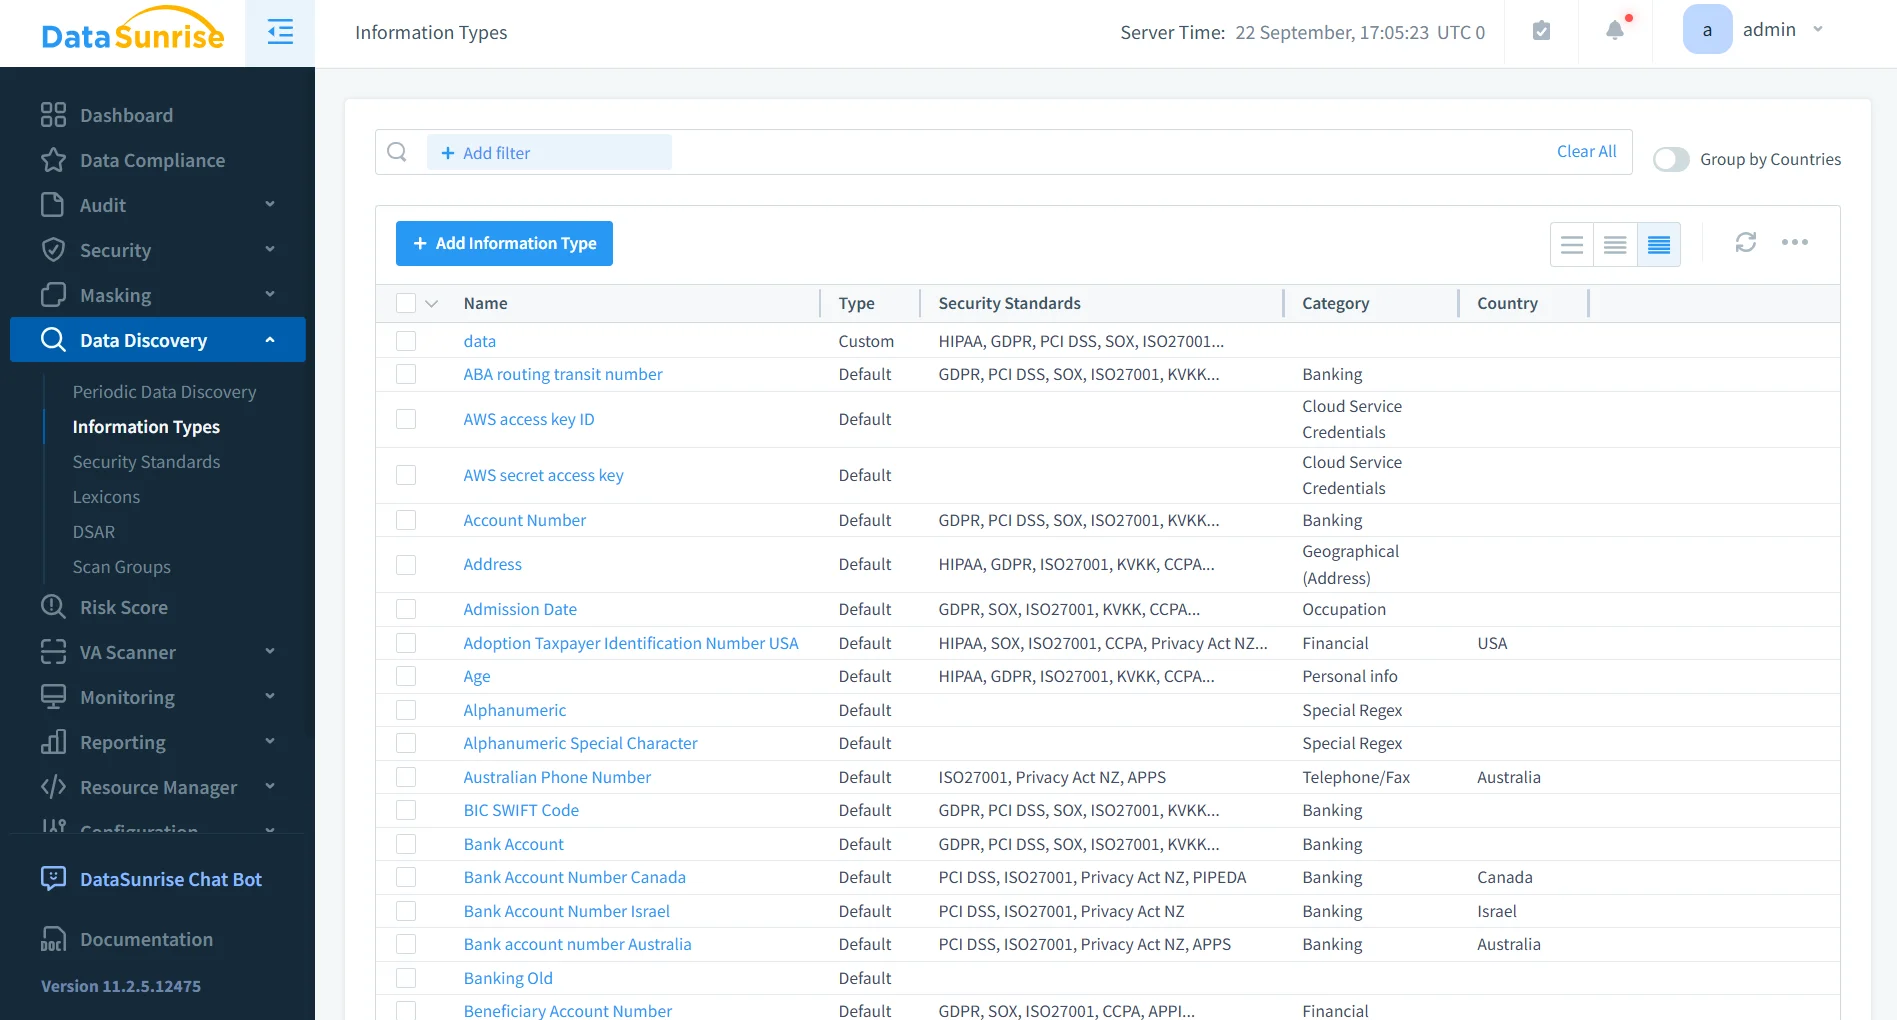
Effective compliance management depends on knowing where sensitive and regulated information resides. DataSunrise Data Discovery scans Amazon Redshift database objects and classifies discovered content using Information Types.
These classifications can include personally identifiable information, payment data, financial records, authentication information, healthcare-related data, and organization-specific sensitive values.
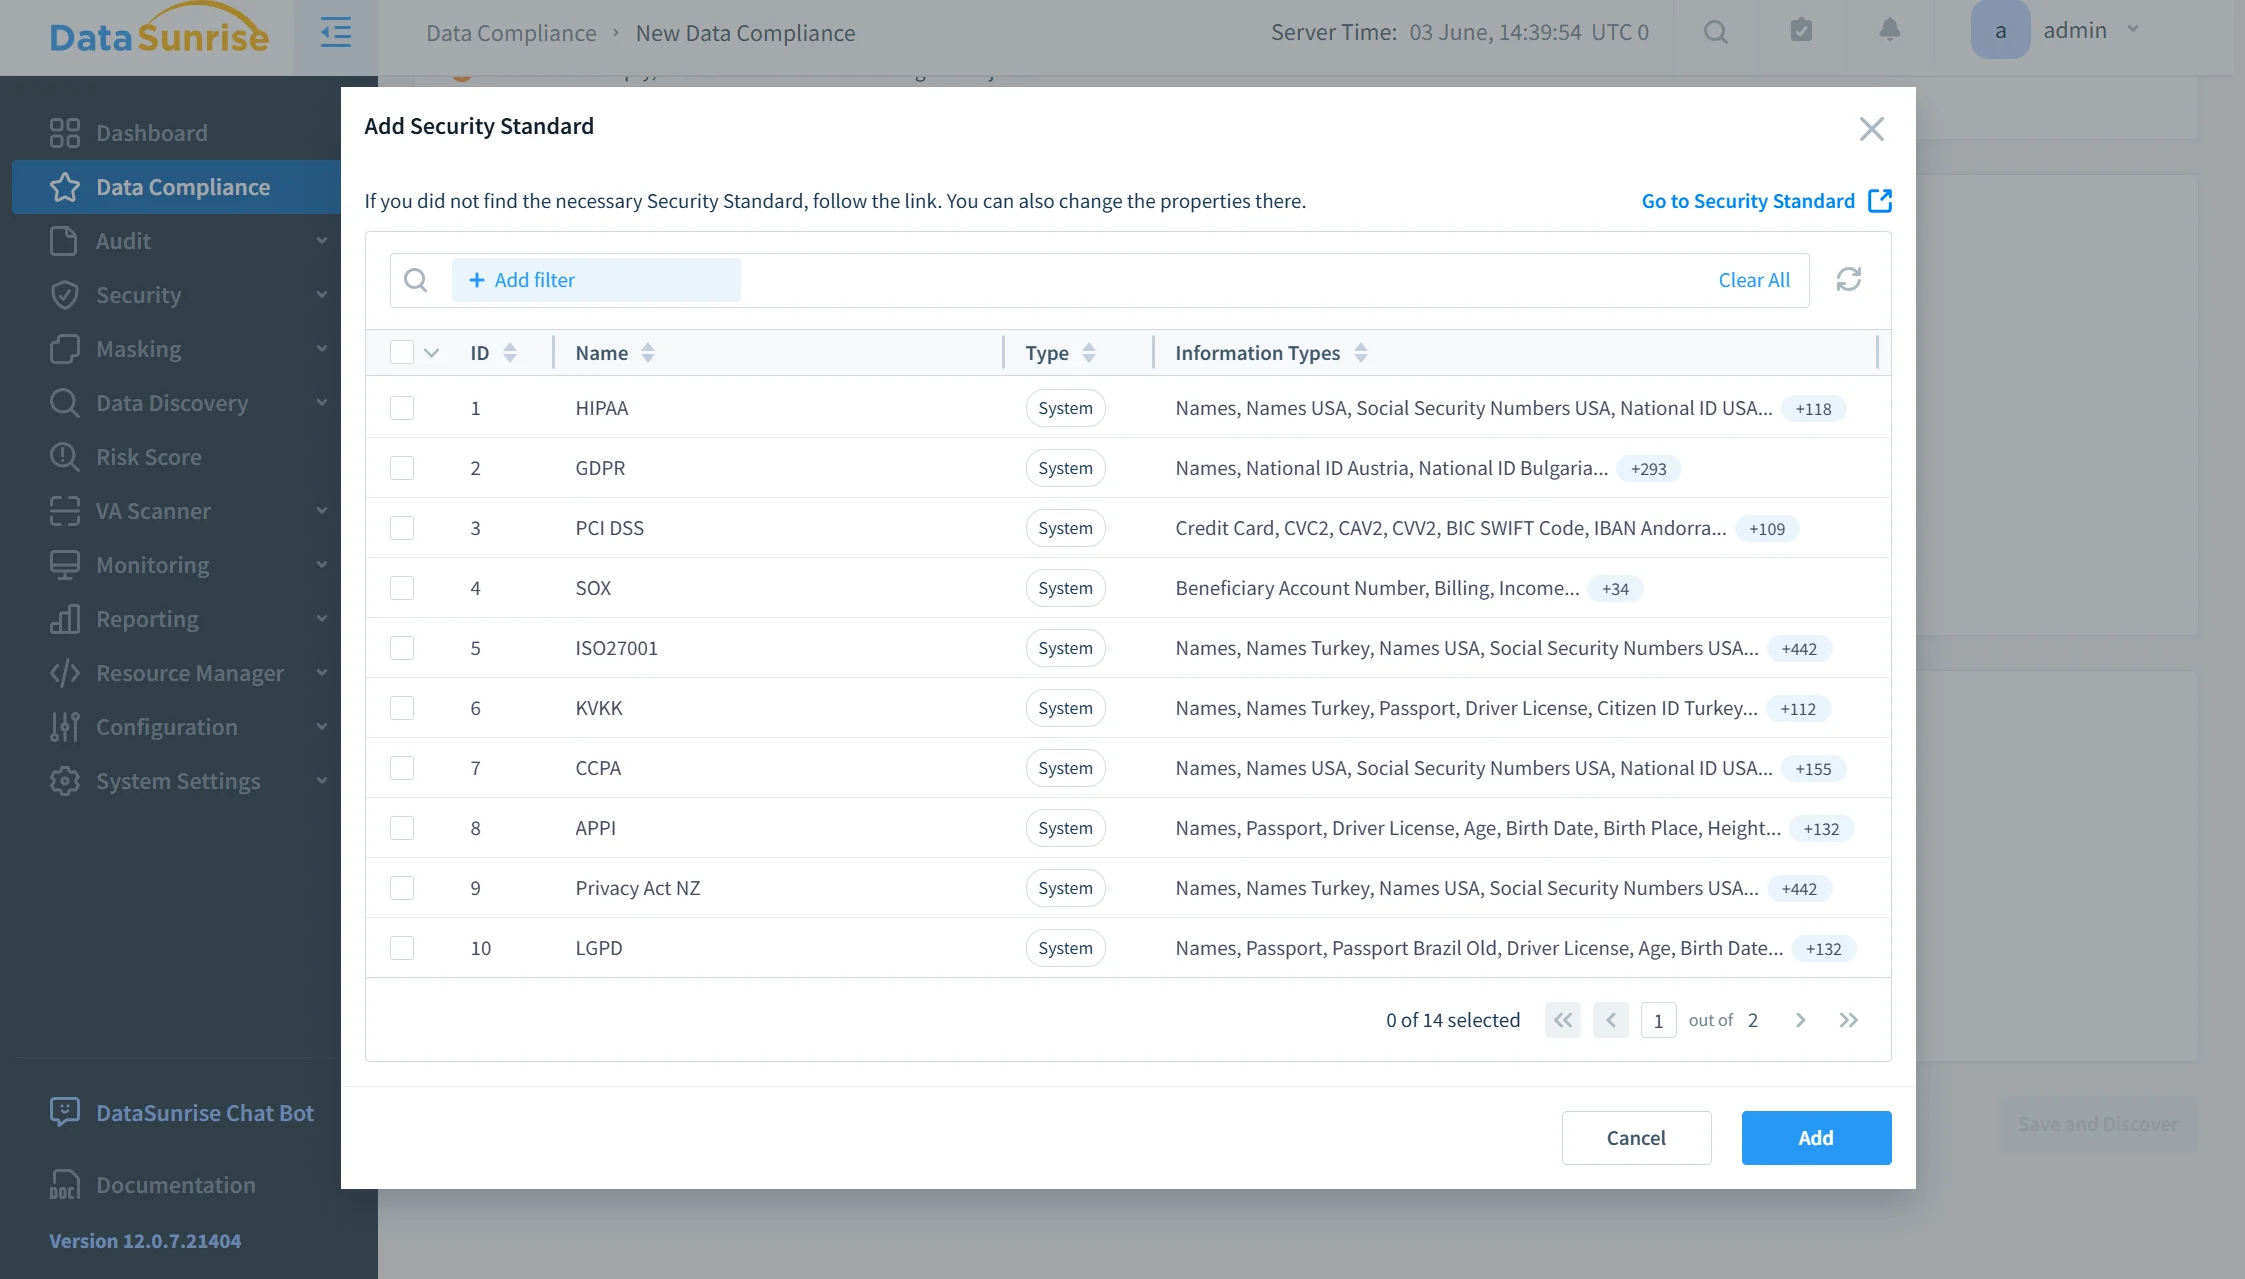
Information Types can also be associated with regulatory frameworks such as GDPR, HIPAA, PCI DSS, SOX, and ISO 27001. Periodic discovery tasks allow organizations to repeat scans as schemas and datasets change.
This creates a more continuous compliance process, helping teams identify newly introduced sensitive information instead of relying only on static inventories.
Automate Compliance Policy Management
After sensitive data is identified, DataSunrise can use those findings within its compliance-management workflow.
Compliance Autopilot, No-Code Policy Automation, Automatic Policy Generation, and Continuous Regulatory Calibration are designed to reduce repetitive administrative work associated with regulations such as GDPR, HIPAA, PCI DSS, and SOX. These capabilities help organizations maintain policies as protected environments evolve.
Rather than managing discovery, auditing, masking, and reporting as separate procedures, compliance teams can coordinate these activities through a centralized framework.
This approach is particularly useful in Amazon Redshift environments where schemas, users, and analytical workloads change frequently.
Monitor Sensitive Data Activity
Sensitive Data Discovery identifies regulated information, while Data Audit provides visibility into how that information is accessed.
DataSunrise audit rules can target specific Amazon Redshift users, database objects, operations, and data conditions. Captured events are available through Transactional Trails, where administrators can review SQL activity, session context, rule matches, and other event details.
Event Tagging can associate audit events with Information Types, allowing compliance teams to understand which categories of sensitive data were involved in particular database actions.
Machine Learning Audit Rules and behavioral analysis can further help prioritize unusual or potentially risky activity. This reduces the need to review every event manually and helps security teams focus on activity that may require investigation.
Reduce Sensitive Data Exposure
Monitoring alone does not prevent unnecessary exposure of regulated information. DataSunrise therefore combines auditing with Dynamic Data Masking and Static Data Masking.
Dynamic Data Masking can modify sensitive values in Amazon Redshift query results according to configured policies while leaving the underlying data unchanged. This allows authorized applications and users to continue working with the database without exposing complete sensitive values where they are not required.
Static Data Masking can create protected copies of production data for development, testing, analytics, or other non-production environments.
By combining discovery and masking, organizations can move from identifying sensitive data to applying protection policies through the same centralized platform. This supports data-minimization practices and reduces unnecessary exposure of regulated information.
Generate Compliance Evidence
Compliance management also requires reliable evidence that controls are operating as expected.
DataSunrise provides report generation for audit activity, discovery results, sessions, security events, and other collected information. Reports can be used to support internal reviews, regulatory assessments, and external audits.
Automated reporting reduces the need to reconstruct evidence manually shortly before an audit. Instead, organizations can maintain a continuous record of monitored activity, discovered sensitive data, and relevant security events.
By centralizing discovery, monitoring, masking, policy management, and reporting, DataSunrise helps Amazon Redshift environments reduce manual compliance effort while maintaining more consistent oversight of regulated data.
Native Amazon Redshift vs. DataSunrise Compliance Management
| Compliance Area | Amazon Redshift | DataSunrise |
|---|---|---|
| Access Control | Native RBAC, RLS, and granular privileges | Centralized security and compliance policies |
| Data Masking | Native Dynamic Data Masking | Dynamic and Static Data Masking |
| Sensitive Data Discovery | Separate classification workflow required | Automated Sensitive Data Discovery |
| Activity Monitoring | System views, CloudWatch, and S3 logging | Centralized Database Activity Monitoring |
| Compliance Automation | Primarily manual configuration | Compliance Autopilot and No-Code Policy Automation |
| Reporting | AWS logs, CloudTrail, and system views | Centralized Audit-Ready Reporting |
Conclusion
Amazon Redshift provides a capable native foundation for compliance management through RBAC, granular privileges, row-level security, Dynamic Data Masking, encryption, database audit logging, CloudWatch, Amazon S3, CloudTrail, and AWS compliance resources. Together, these capabilities enable organizations to define access controls, protect sensitive information, and retain important compliance evidence.
However, effective Amazon Redshift Compliance Management is a continuous process. Organizations must repeatedly locate regulated information, review permissions, monitor sensitive activity, detect policy gaps, limit unnecessary exposure, and demonstrate that required controls remain aligned with applicable data compliance regulations.
DataSunrise extends this framework with Sensitive Data Discovery, Compliance Autopilot, Automatic Policy Generation, Continuous Regulatory Calibration, Machine Learning Audit Rules, centralized Database Activity Monitoring, Risk Scoring, Dynamic and Static Data Masking, and Audit-Ready Reporting.
By connecting classification, monitoring, protection, and compliance evidence within a unified workflow, organizations can reduce manual compliance effort while maintaining stronger visibility over sensitive Amazon Redshift data.
Protect Your Data with DataSunrise
Secure your data across every layer with DataSunrise. Detect threats in real time with Activity Monitoring, Data Masking, and Database Firewall. Enforce Data Compliance, discover sensitive data, and protect workloads across 50+ supported cloud, on-prem, and AI system data source integrations.
Start protecting your critical data today
Request a Demo Download Now